Hi there,
Quick blog post on the VM “Bobby” which is once of the nicest VM I did so far.
The first step is always the same: discovering the machine on the network. To do so:
$ nmap -sV 192.168.1.1/24
I managed to retrieve the IP address: 192.168.1.11.
Let’s start to fingerprint the different services to exploit it.
Then, I used Nmap to retrieve the services running:
$ nmap -sV 192.168.1.11

Starting Nmap 6.46 ( http://nmap.org ) at 2014-05-15 20:54 CEST
Nmap scan report for 192.168.1.11
Host is up (0.00037s latency).
Not shown: 997 filtered ports
PORT    STATE  SERVICE VERSION
21/tcp  open   ftp     Microsoft ftpd
80/tcp  open   http    Microsoft IIS httpd 5.1
443/tcp closed https
Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows

Service detection performed. Please report any incorrect results at http://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 12.35 seconds
Using Nikto as well:
... ➦EDIT: Added statistics of max-age option.
... ➦This post deals with some research I just did regarding (Blind) HQL injections with H2 as the DataBase Management System.
First, you should read this post which gives some really useful information regarding HQL injections in general: HQL for pentesters.
During the assessment, I checked the API calls by using Burp as a proxy and one call was:
http://application/API/Users/?req=id=1
The output was a JSON response, such as:
[{user: "admin", id: "1", firstName:"Admin"}]
If you changed the id with the numeric value 2, and so on.. it was working.
... ➦Hey,
Just a quick post to give you the link to my slides for BSides London today: Here Don’t hesitate if you have any feedback, or any good feature.
You can reach me either on Github and Twitter
Just few words about the conference which was absolutely amazing. Some really great people were here, good atmosphere and people were really helpful.
For sure, I’ll attend it next year.
Cheers,
This post contains the steps to get a root shell with bWapp VM
As always, we need to discover where the machine is on our network. To do so, let’s use Nmap:
nmap -sP 192.168.1.1/24
After getting the IP address (192.168.1.10), we need to do some fingerprinting.
nmap -sV 192.168.1.10
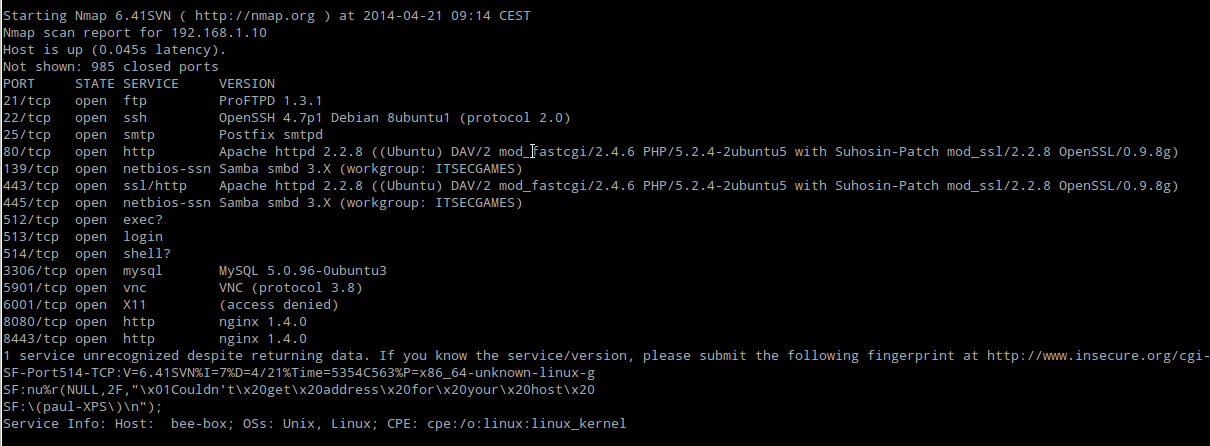
Fig. Nmap scan result
A lot of services were open, such as: VNC, FTP, etc.
As I saw it in the scan report, I decided to scan the port 80 with Nikto.
... ➦This post contains the steps to get a root shell with Scream VM
This VM can he found here. Have a look to find even more VMs. But before starting the report, I’d like to congratulate g0tmi1k for his awesome tool : VulnInjector.
Ok, let’s do this write-up !
As always, we need to discover where the machine is on our network. To do so, let’s use Nmap:
nmap -sP 192.168.1.1/24
After getting the IP address (192.168.1.2), we need to do some fingerprinting.
... ➦This post contains the steps to get a root shell with Exploit KB Vulnerable Web App 1 VM
This VM can he found here. Have a look to find even more VMs
First, we need to discover where the machine is on our network. To do so, let’s use Nmap:
nmap -sP 192.168.1.1/24
After getting the IP address, we need to do some fingerprinting.
nmap -sV 192.168.1.23
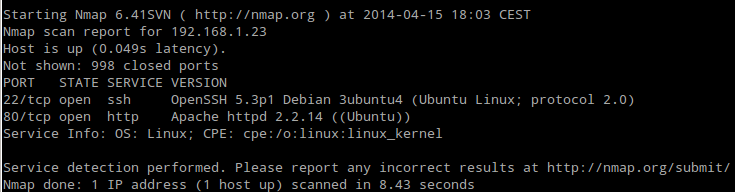
Fig. Nmap scan result
... ➦This post contains the steps to get a root shell with Kioptrix level 2 VM
This VM can he found here. Have a look to find even more VMs
First, we need to discover where the machine is on our network. To do so, let’s use Nmap:
nmap -sP 192.168.1.1/24
After getting the IP address, we need to do some fingerprinting.
nmap -sV 192.168.1.42
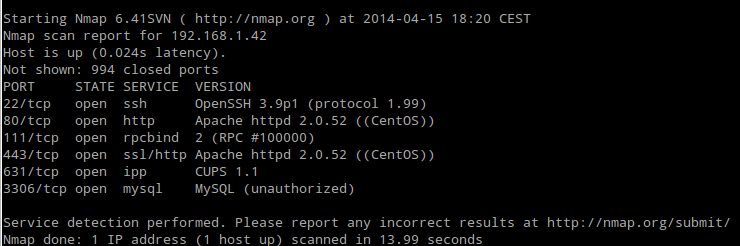
Fig. Nmap scan result
As I saw it in the scan report, I decided to scan the port 80 with Nikto.
... ➦This post contains the steps to get a root shell with Kioptrix level 1 VM
This VM can he found here. Have a look to find even more VMs
First, we need to discover where the machine is on our network. To do so, let’s use Nmap:
nmap -sP 192.168.1.1/24
After getting the IP address, we need to do some fingerprinting.
nmap -sV 192.168.1.2
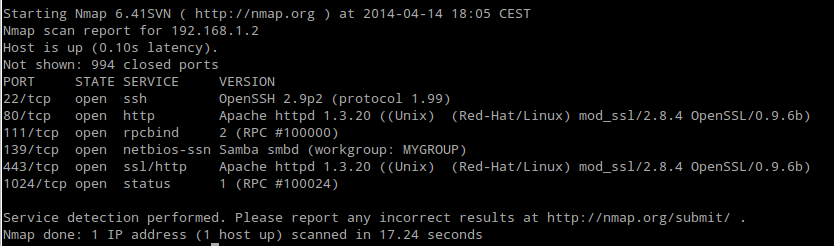
Fig. Nmap scan result
As I saw it in the scan report, I decided to scan on the port 80 and 443 with DirBuster and Nikto.
... ➦Hey there,
Quick blog post for the first VM I created to experiment some of your pentesting skills.
The idea grew up when I developed some security tools (especially the one (CSRFT) I presented at BSides London few weeks ago) to create a legal environment where you could try it out.
I really liked creating this Boot2root VM. So, I’ll create few more that will rely on each other so keep the flags because you’ll need it for the next ones.
... ➦